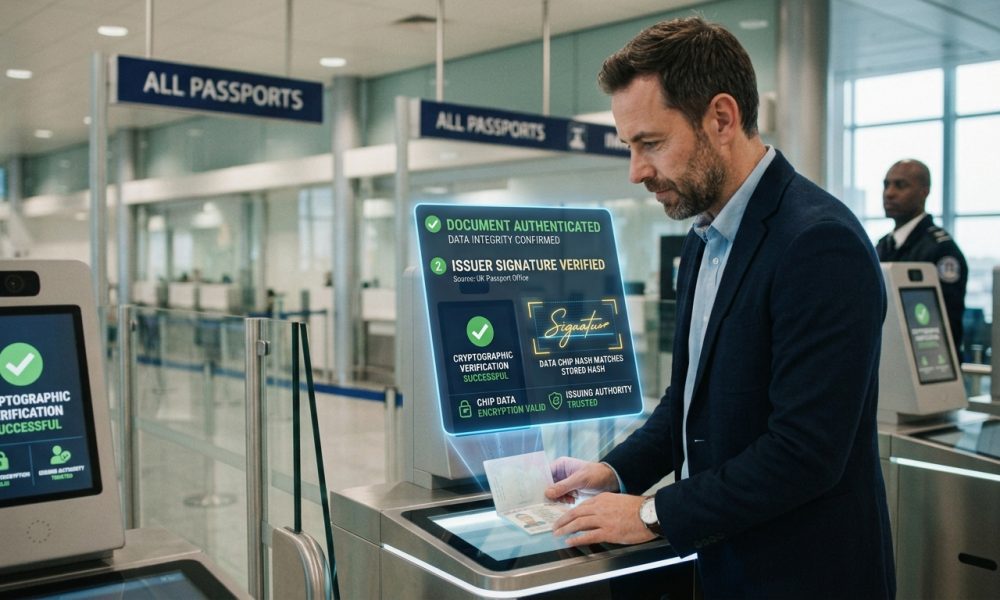
Cryptographic verification helps establish whether protected chip Information remains unchanged and comes from a trusted issuer.
WASHINGTON, DC, October 10, 2026 — As international airports increasingly rely on automated passport inspection and biometric identity verification, an invisible security mechanism embedded within electronic travel documents plays a critical role in helping border authorities distinguish government-issued identity Information from potentially altered or unauthorized electronic records.
Known as a digital signature, this cryptographic security feature lets compatible inspection systems verify that the Information stored in an electronic passport originated from a recognized issuing authority and hasn’t been modified since the government digitally signed the protected data.
Unlike traditional passport security features that officers examine through specialized lighting, magnification, or physical inspection, digital signatures operate through mathematical verification processes that connect electronically stored identity Information with cryptographic certificates associated with the issuing country.
These security mechanisms form part of the international electronic passport framework established by the International Civil Aviation Organization, whose technical specifications support interoperable document Authentication across countries using different border management equipment and national immigration infrastructures.
The growing importance of these safeguards reflects a fundamental reality of modern international travel: increasingly sophisticated electronic passports must protect not only the physical identity document but also the reliability of the digital Information relied on during immigration inspections.
The Electronic Passport Contains More Than Biographical Information
A modern electronic passport includes a contactless integrated circuit that stores electronically encoded identity Information, allowing compatible inspection systems to retrieve protected data without relying solely on the details printed on the document’s Identification page.
The Information typically includes the passport holder’s name, nationality, date of birth, document number, and a digitally stored facial photograph, together with additional technical structures that help authorized systems assess the document’s electronic integrity.
Although travelers generally associate electronic passport technology with biometric facial recognition, the embedded chip also contains security Information designed to establish whether the stored identity records remain consistent with those approved during official document issuance.
Without an appropriate Authentication mechanism, an inspection system could potentially read electronically presented identity Information without independently establishing whether the underlying data had been modified or whether it originated from a legitimate government issuer.
Digital signatures address this challenge by providing cryptographic evidence that connects protected passport Information with the issuing authority’s trusted signing infrastructure, creating an additional layer of confidence beyond ordinary electronic data retrieval.
The distinction becomes particularly important when border officials compare the electronically stored facial photograph with a live Camera Image, because an unverified electronic portrait cannot provide the same assurance as an authenticated government-issued reference Image.
How Digital Signatures Protect Passport Information
Digital signatures use asymmetric cryptography, a method involving mathematically related public and private keys that lets one party sign electronic Information while another party verifies the resulting signature.
During passport production, an authorized government signing system processes specified electronic Information using an approved cryptographic algorithm and a protected private signing key controlled within the issuing authority’s security infrastructure.
The resulting digital signature becomes associated with the passport’s protected electronic Information, allowing inspection systems with the corresponding public verification key to verify that the signed material remains authentic and unchanged.
If an unauthorized alteration changes protected Information after issuance, cryptographic verification should detect an inconsistency between the Information currently presented and the signed values originally established by the issuing authority.
According to the International Civil Aviation Organization’s electronic passport guidance, digital signatures connect protected travel document Information with government-issued cryptographic certificates, enabling border authorities to verify both the Authenticity and integrity of electronically stored passport data.
Importantly, digital signing does not mean that the identity Information becomes unreadable or that all personal details are encrypted using the same mechanism, because Authentication and confidentiality serve different security purposes.
Instead, the signature provides evidence of the origin and integrity of specific electronic records. At the same time, separate access-control and secure communication protocols can protect Information exchanges between the passport chip and inspection equipment.
The Document Security Object Connects Identity Data With Cryptographic Evidence
Within an electronic passport, an important technical structure called the Document Security Object contains Information used to authenticate protected data groups stored in the document’s integrated electronic circuit.
Often identified by its technical file designation, EF.SOD, this structure contains cryptographic hash values for covered data groups, along with a digital signature that protects those values against unauthorized changes.
A cryptographic hash transforms electronic Information into a fixed-length mathematical representation, allowing inspection software to detect changes without comparing it to a separately stored copy of the entire original record.
When a border inspection system reads the passport, it can calculate fresh hash values from the retrieved Information and compare those results with the authenticated values recorded in the Document Security Object.
Matching values help demonstrate that the relevant data groups remain consistent with the Information included in the original signed security structure, provided the inspection system has also successfully authenticated the digital signature itself.
This distinction matters because matching hash values alone do not establish government origin unless the accompanying signature and certification chain provide sufficient evidence that a trusted signing authority produced the reference values.
The Country Signing Certification Authority Establishes Trust
Every government issuing internationally interoperable electronic passports requires a cryptographic trust infrastructure that lets authorized inspection systems establish the origin of digital signatures on its travel documents.
At the foundation of this infrastructure is the Country Signing Certification Authority (CSCA), the principal national trust anchor for electronic passport signature verification.
The CSCA maintains highly sensitive signing capabilities and issues certificates that establish trust in subordinate document signing systems responsible for producing the digital signatures incorporated into individual passports.
This arrangement creates a hierarchical relationship between the issuing government’s foundational signing authority and the operational certificates used to authenticate passports produced for its citizens and other eligible document holders.
For receiving countries, independently trusting the appropriate CSCA certificate provides a basis for assessing whether a passport’s document signing certificate genuinely belongs to the government authority represented within the electronic security structure.
The Authenticity of that foundational certificate is therefore essential, because an inspection system cannot establish reliable government provenance merely by accepting a certificate presented alongside the passport without validating its trusted origin.
Document Signer Certificates Authenticate Individual Passport Signatures
Below the national signing authority, governments use Document Signer Certificates, commonly known as DSCs, to support signing and later verifying electronic passport Information during document production and international inspection.
Each Document Signer Certificate contains a public verification key associated with the corresponding document-signing operation, along with certification Information that links the signer to the issuing authority’s trusted national infrastructure.
When a passport undergoes electronic inspection, compatible verification software uses the applicable public key to examine the document signature and determine whether the trusted CSCA can authenticate the Document Signer Certificate.
This sequence establishes a cryptographic chain of trust from the electronic Information stored in the passport to the government certification authority that authorizes the document-signing system.
Because governments regularly issue new passports and rotate operational signing credentials under their security policies, inspection authorities must manage multiple valid and historical certificates rather than rely on a single permanent signing key.
The system’s effectiveness depends on protecting private signing keys during issuance, distributing authentic public certificates to inspection authorities, and maintaining procedures for certificate updates, expiration, and security incidents.
Passive Authentication Is the Core Verification Process
The internationally recognized procedure for verifying electronic passport signatures and protected data integrity is Passive Authentication, a process performed by compatible inspection systems using the document’s signed Information and trusted public certificates.
During this procedure, the inspection system retrieves the relevant security Information from the passport chip, verifies the document signature, evaluates the associated certification chain, and compares authenticated hash values against the protected data groups.
The Government of Canada describes Passive Authentication within its electronic passport security framework as a means of verifying that digitally stored personal Information and the facial photograph remain authentic and unaltered.
A successful result provides evidence that the authenticated data groups remain consistent with the material signed during issuance and that the signature can be associated with the trusted issuing authority.
However, Passive Authentication should not be interpreted as confirmation that every aspect of the physical passport is genuine, because the procedure specifically addresses the origin and integrity of electronically protected Information.
Additional physical inspection, biometric comparison, document status verification, and immigration eligibility checks remain separate functions that authorities may perform when evaluating the passport and the person presenting it.
Why the ICAO Public Key Directory Matters
International travel creates a significant challenge for electronic passport Authentication because immigration authorities regularly encounter documents issued by numerous governments, each maintaining its own cryptographic certificates and document signing infrastructure.
For digital signatures to provide meaningful cross-border Protection, receiving countries must obtain reliable verification Information from issuing authorities and manage that Information within inspection systems that can recognize trusted international certificates.
The International Civil Aviation Organization established the Public Key Directory (PKD) to facilitate structured international exchange of cryptographic materials used in electronic passport and related travel document Authentication.
Through the ICAO Public Key Directory, participating authorities can access relevant Document Signer Certificates, certificate revocation Information, and signed master lists containing national trust certificates, supporting more consistent electronic travel document verification.
The directory does not function as a centralized database containing every passport holder’s name, photograph, or travel history because its principal purpose is to distribute the cryptographic Information needed to authenticate electronic documents.
Moreover, participation in the directory is not the only way to obtain trusted certificates, since governments can also exchange relevant materials through bilateral arrangements and other appropriately authenticated channels.
This distinction explains why electronic passport verification requires more than simply checking whether a certificate appears in a particular online repository, because receiving authorities must establish trust in the certificate itself.
Certificate Revocation Protects Against Compromised Signing Credentials
Cryptographic trust systems must also account for circumstances in which a government discovers that a signing credential has been compromised, improperly issued, or otherwise rendered unsuitable for continued reliance during document Authentication.
Certificate Revocation Lists provide a mechanism for communicating Information about certificates that issuing authorities have withdrawn from trust, helping receiving systems identify credentials that should no longer be accepted under applicable verification policies.
These lists differ from databases that report individual lost or stolen passports because certificate revocation concerns the security of signing credentials rather than the administrative status of a specific travel document.
A compromised document-signing key could undermine confidence in numerous documents signed with that credential, making certificate management and incident response key responsibilities for passport-issuing authorities and border inspection operators.
A certificate issue may require additional technical evaluation rather than automatically assuming every associated passport is counterfeit, particularly when circumstances involve historical signing periods or system configuration issues.
Similarly, a certificate’s expiration does not automatically invalidate legitimately signed passports. At the same time, the credential was authorized, because electronic passport verification must account for historical issuance and applicable certificate validation policies.
Digital Signatures Do Not Automatically Detect Cloned Passport Chips
One important limitation of Passive Authentication is that electronically signed passport Information could be copied without changing the protected data, allowing a copied dataset to retain a mathematically valid original signature.
Because Passive Authentication verifies the integrity and origin of signed Information rather than independently proving possession of the original physical chip, a copied dataset may pass signature verification under some circumstances.
To address this separate security concern, electronic passport technologies can incorporate additional mechanisms, such as Active Authentication or Chip Authentication, that provide stronger evidence that the chip has the cryptographic capabilities associated with the original document.
These mechanisms generally rely on challenge-response procedures or cryptographic key agreements that help inspection systems distinguish an authentic chip from an unauthorized reproduction containing copied electronic identity records.
The availability of these protections depends on passport generation, issuing-country implementation, supported technical protocols, and the capabilities of the equipment performing border inspection.
Accordingly, a successful Passive Authentication result confirms the authenticity and integrity of signed data rather than proving the physical chip could not have been duplicated.
Electronic Signature Verification Is Separate From Facial Recognition
Digital signatures and biometric facial recognition complement one another during electronic passport inspection. Still, the technologies answer fundamentally different questions about document integrity and the identity of the traveler presenting it.
Signature verification confirms that protected electronic Information originated from a trusted issuing authority and has not changed. At the same time, facial recognition compares biometric characteristics extracted from a live Image with an appropriate reference photograph.
When an inspection system authenticates the passport’s electronically stored portrait, that verified Image can provide a more reliable reference for biometric comparison than a photograph whose electronic origin and integrity have not been established.
A successful facial comparison does not independently prove that the underlying passport data was legitimately signed, just as a valid digital signature does not establish that the person presenting the document is its rightful holder.
Border authorities therefore gain stronger assurance when these functions operate together, combining cryptographic evidence about the travel document with biometric evidence about the relationship between the passenger and the authenticated identity record.
Even where both procedures succeed, authorities may still need to evaluate separate immigration records, travel permissions, document status Information, and relevant security requirements before authorizing the passenger to cross the border.
What Happens When Authentication Cannot Be Completed
Electronic passport Authentication does not always succeed, and unsuccessful verification can result from several technical or administrative circumstances that do not necessarily indicate deliberate document manipulation.
Inspection equipment may struggle to read the contactless chip, retrieve the necessary security files, obtain trusted certificates, or interpret a document issued with technical configurations unsupported by the inspection system.
A missing certificate can prevent a receiving authority from completing an otherwise legitimate trust-chain assessment, even when the passport was properly produced and digitally signed by its issuing government.
Likewise, a failure to read electronic Information should not automatically be treated as proof that the stored Information has been altered, because communication difficulties and physical chip damage can produce different technical outcomes.
A genuine signature mismatch, however, raises a more direct integrity concern because the cryptographic evidence does not agree with the protected Information presented for verification under the relevant signing and Authentication rules.
Border authorities may respond through established exception-handling procedures, additional document examination, consultation of alternative verification resources, or referral to an immigration officer for further assessment.
Smartphone Passport Applications Can Perform Signature Checks
Modern smartphones with compatible contactless communication hardware can interact with electronic passports through specialized applications that read supported chip Information and perform selected cryptographic verification procedures.
Depending on the Application’s capabilities and available certificate resources, a mobile passport reader may retrieve biographical Information, display the electronically stored facial photograph, and evaluate the digital signature protecting relevant data groups.
These applications can provide useful technical insights into the integrity of passport data. However, their verification results depend on supported protocols, certificate management practices, Application configuration, and the accuracy of the displayed status Information.
A smartphone Application that successfully reads identity Information has not necessarily completed Passive Authentication, because electronic data retrieval and cryptographic verification are distinct operations that require different supporting resources.
Similarly, an Application that reports an incomplete certificate chain may lack trusted verification materials rather than detect a counterfeit document, so the exact technical explanation matters when interpreting the result.
Private passport scanning tools also cannot replace official border inspection, because immigration authorities may have access to additional government records, specialist equipment, and legally authorized verification procedures unavailable to consumer applications.
A Valid Digital Signature Does Not Guarantee a Valid Passport
The most important distinction in electronic passport security concerns the difference between cryptographic authenticity and a document’s continuing legal validity under its issuing government.
A passport may contain correctly signed electronic information but have since expired, been canceled, or been reported stolen, because those administrative events do not automatically alter the cryptographic signature embedded at issuance.
Passive Authentication therefore cannot independently determine whether the issuing government currently considers the passport acceptable for international travel, so authorities must consult appropriate document status Information where such checks apply.
Similarly, a properly authenticated electronic passport does not automatically establish eligibility to enter another country, since visa requirements, residence permissions, immigration restrictions, and other admission conditions operate independently of the signature.
This distinction matters especially for travelers who mistakenly assume that successful smartphone Authentication or automated chip reading shows full government approval of their passport or international travel plans.
Cryptographic verification establishes confidence in defined electronic Information, while the broader assessment of passport validity and international admissibility depends on separate legal, administrative, and border management procedures.
Why Consistent International Standards Are Essential
The effectiveness of electronic passport Authentication depends heavily on international interoperability, because a passport issued under one national infrastructure must remain understandable and verifiable by inspection systems operated in numerous other jurisdictions.
ICAO Document 9303 sets technical specifications that support this interoperability, covering key aspects of machine-readable travel documents, electronic data structures, cryptographic Protection, and the mechanisms used to authenticate electronic passport Information.
Common standards let different governments and technology providers develop compatible inspection equipment while retaining responsibility for certificate issuance, Information security practices, and domestic border control policies.
Nevertheless, national implementation differences remain possible, particularly regarding supported Authentication protocols, certificate trust decisions, inspection workflows, and the additional measures authorities employ when standard electronic verification cannot be completed.
International cooperation must therefore extend beyond adopting compatible passport chips to include reliable certificate distribution, operational training, security governance, and mechanisms to respond to compromised or outdated cryptographic credentials.
These requirements matter more as governments expand automated border processing and rely on authenticated electronic identity data to speed passenger clearance without eliminating necessary security and immigration controls.
The Future of Cryptographic Passport Authentication
As electronic identity systems evolve, governments are expected to place greater emphasis on reliable cryptographic trust infrastructures that support secure digital credentials, automated inspection, and interoperable identity verification.
Emerging travel technology may change how passengers present identity Information. Still, establishing trusted origins and detecting unauthorized modification will remain central to the security of digitally managed borders.
Future cryptographic standards, including approaches designed to address longer-term computing threats, may eventually influence how issuing authorities protect signing credentials and maintain confidence in electronic travel documents.
Any transition toward updated algorithms would require careful international coordination, because passport issuance systems, document lifespans, inspection equipment, and certificate distribution networks must remain compatible throughout extended periods of technological change.
For border agencies, the challenge is maintaining dependable Authentication while accommodating passports issued under different generations of technical standards and national policies governing electronic identity document security.
For travelers, the ongoing evolution of these systems underscores that electronic passport Authenticity involves more than an NFC chip, a readable digital photograph, or a successful response from a passport-scanning Application.
Digital Trust Has Become a Foundation of Modern Border Security
Digital signatures have transformed passport Authentication by giving receiving authorities a standardized way to verify that electronically stored identity Information remains unchanged and can be traced through trusted cryptographic credentials to its issuing government.
Through Passive Authentication, national signing authorities, document-signing certificates, and international certificate-exchange arrangements, modern border systems can establish meaningful evidence of the provenance and integrity of protected travel-document Information.
These safeguards operate alongside biometric verification, physical document inspection, administrative status checks, and immigration screening rather than replacing the independent functions that authorities must perform before permitting international entry.
The ability to authenticate electronic identity records is therefore a foundational component of contemporary border management, especially as automated systems increasingly rely on digital Information to evaluate travel documents presented by international passengers.
Ultimately, a passport’s digital signature matters not because it makes the document impossible to counterfeit, but because it provides a reliable mathematical basis for detecting unauthorized changes and building trust in government-issued electronic identity Information.